Fortify Your Vendor Ecosystem. Eliminate Third-Party Risk.

TPRM SERVICES
Strengthen vendor security, ensure regulatory compliance and mitigate supply chain risks with an advanced Third-Party Risk Management (TPRM) program built for banks, NBFCs and financial institutions.
TPRM SERVICES

Third-Party Risk Management (TPRM) Services to Secure Your Vendor Ecosystem

Our TPRM services provide continuous visibility into vendor security posture, enabling you to identify high-risk vendors, strengthen governance, and maintain audit-ready compliance.
Managing Third-Party Risks

Modern organisations depend on vendors, suppliers, and cloud providers to support business operations. However, every third-party relationship introduces potential cybersecurity and compliance risks. Our Third-Party Risk Management (TPRM) solutions help identify, assess, and monitor vendor risks to strengthen overall security and resilience.

Strengthening Vendor Security

Third-party breaches can lead to data exposure, operational disruption, and compliance challenges. We help organisations assess vendor security posture, identify critical gaps, and implement risk-based governance to reduce supply chain risks and improve business resilience.

Managing Third-Party Risks

Modern organisations depend on vendors, suppliers, and cloud providers to support business operations. However, every third-party relationship introduces potential cybersecurity and compliance risks. Our Third-Party Risk Management (TPRM) solutions help identify, assess, and monitor vendor risks to strengthen overall security and resilience.

Strengthening Vendor Security

Third-party breaches can lead to data exposure, operational disruption, and compliance challenges. We help organisations assess vendor security posture, identify critical gaps, and implement risk-based governance to reduce supply chain risks and improve business resilience.

Trust Through Visibility

Are your Vendors introducing Hidden Risks?

Continuously assess, monitor, and manage third-party risks across your vendor ecosystem.

Do you have complete visibility into your vendor ecosystem?

Nearly 60% of organizations experienced a third-party data breach, highlighting the need for continuous vendor visibility and risk oversight.

Can your third-party assessments withstand regulatory scrutiny?

Manual vendor assessments often create inconsistent results, compliance gaps, and audit challenges as regulatory expectations continue to increase.

Are your Vendors introducing Hidden Risks?

Continuously assess, monitor, and manage third-party risks across your vendor ecosystem.

Do you have complete visibility into your vendor ecosystem?

Nearly 60% of organizations experienced a third-party data breach, highlighting the need for continuous vendor visibility and risk oversight.

Can your third-party assessments withstand regulatory scrutiny?

Manual vendor assessments often create inconsistent results, compliance gaps, and audit challenges as regulatory expectations continue to increase.

How

tiny

crows

helps you?

Our TPRM engagements are designed to answer one core question:
 Can your organization confidently manage and mitigate risks introduced by third-party vendors and partners?
We help you move from reactive vendor assessments to continuous risk visibility by identifying security gaps, evaluating vendor security posture, and strengthening governance across your third-party ecosystem to reduce business and compliance risks

Our Process

Our

Products &

Features

Strengthening Trust Across Your Vendor Ecosystem

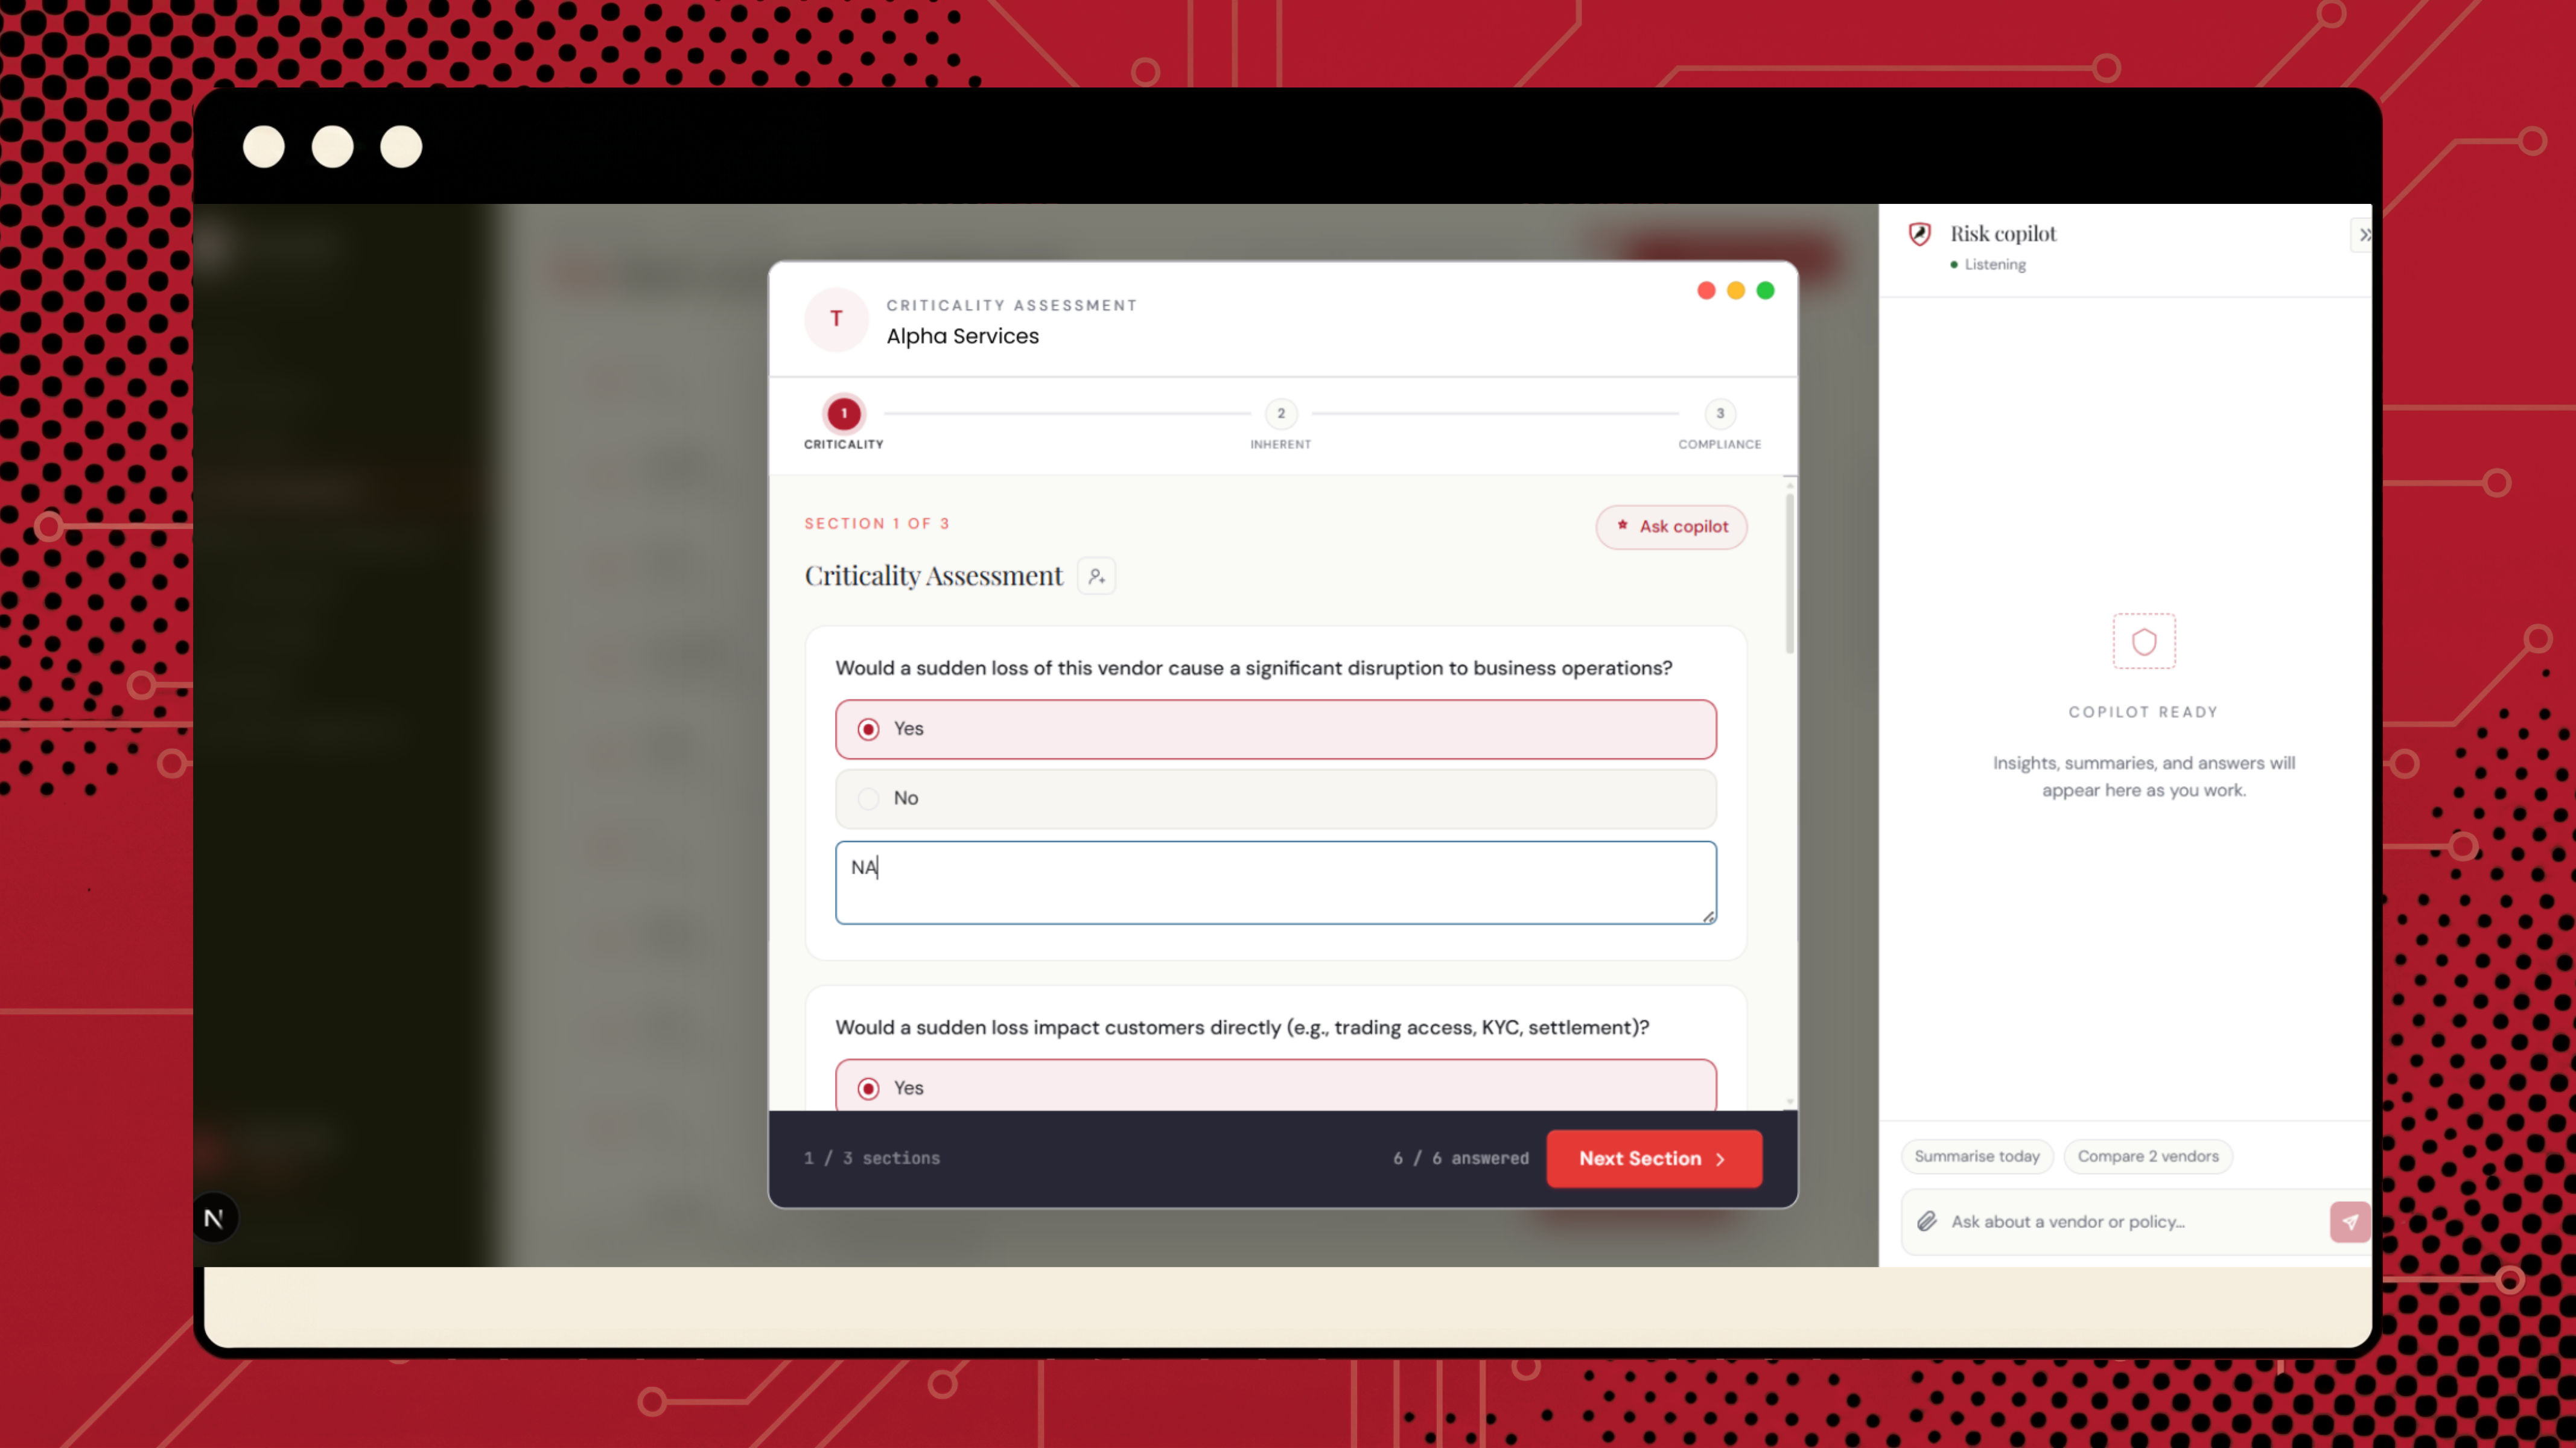
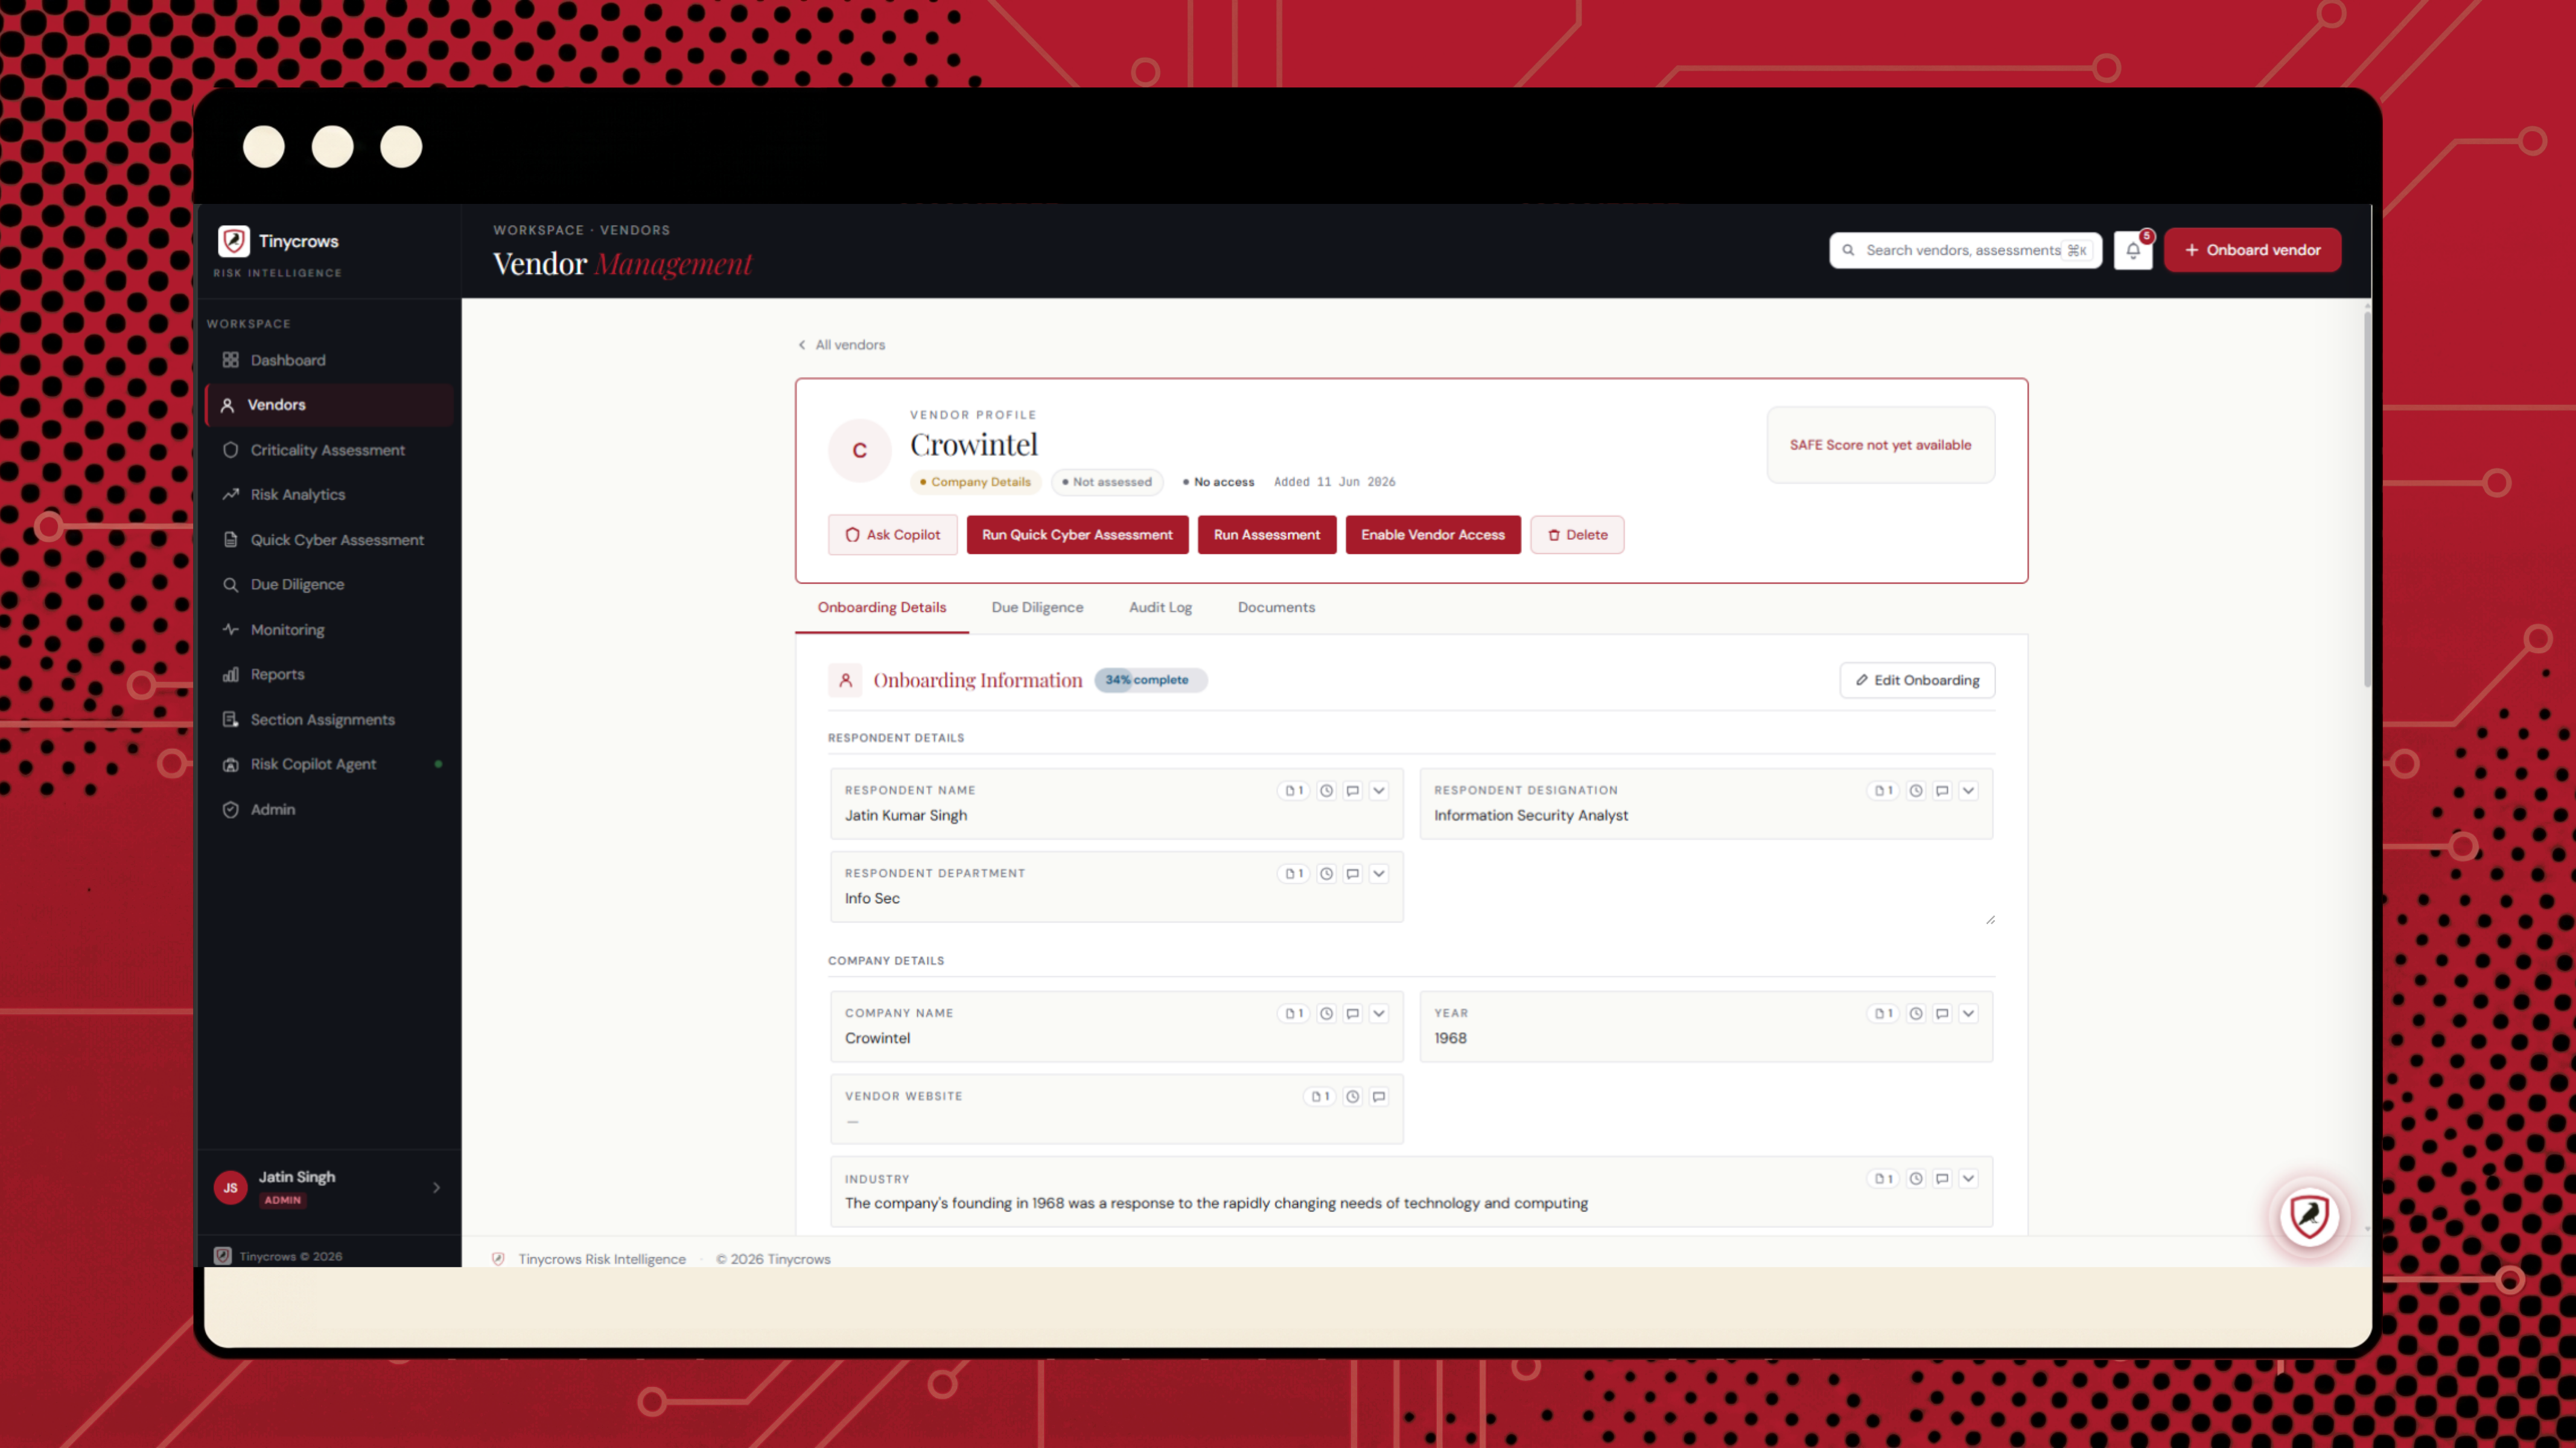
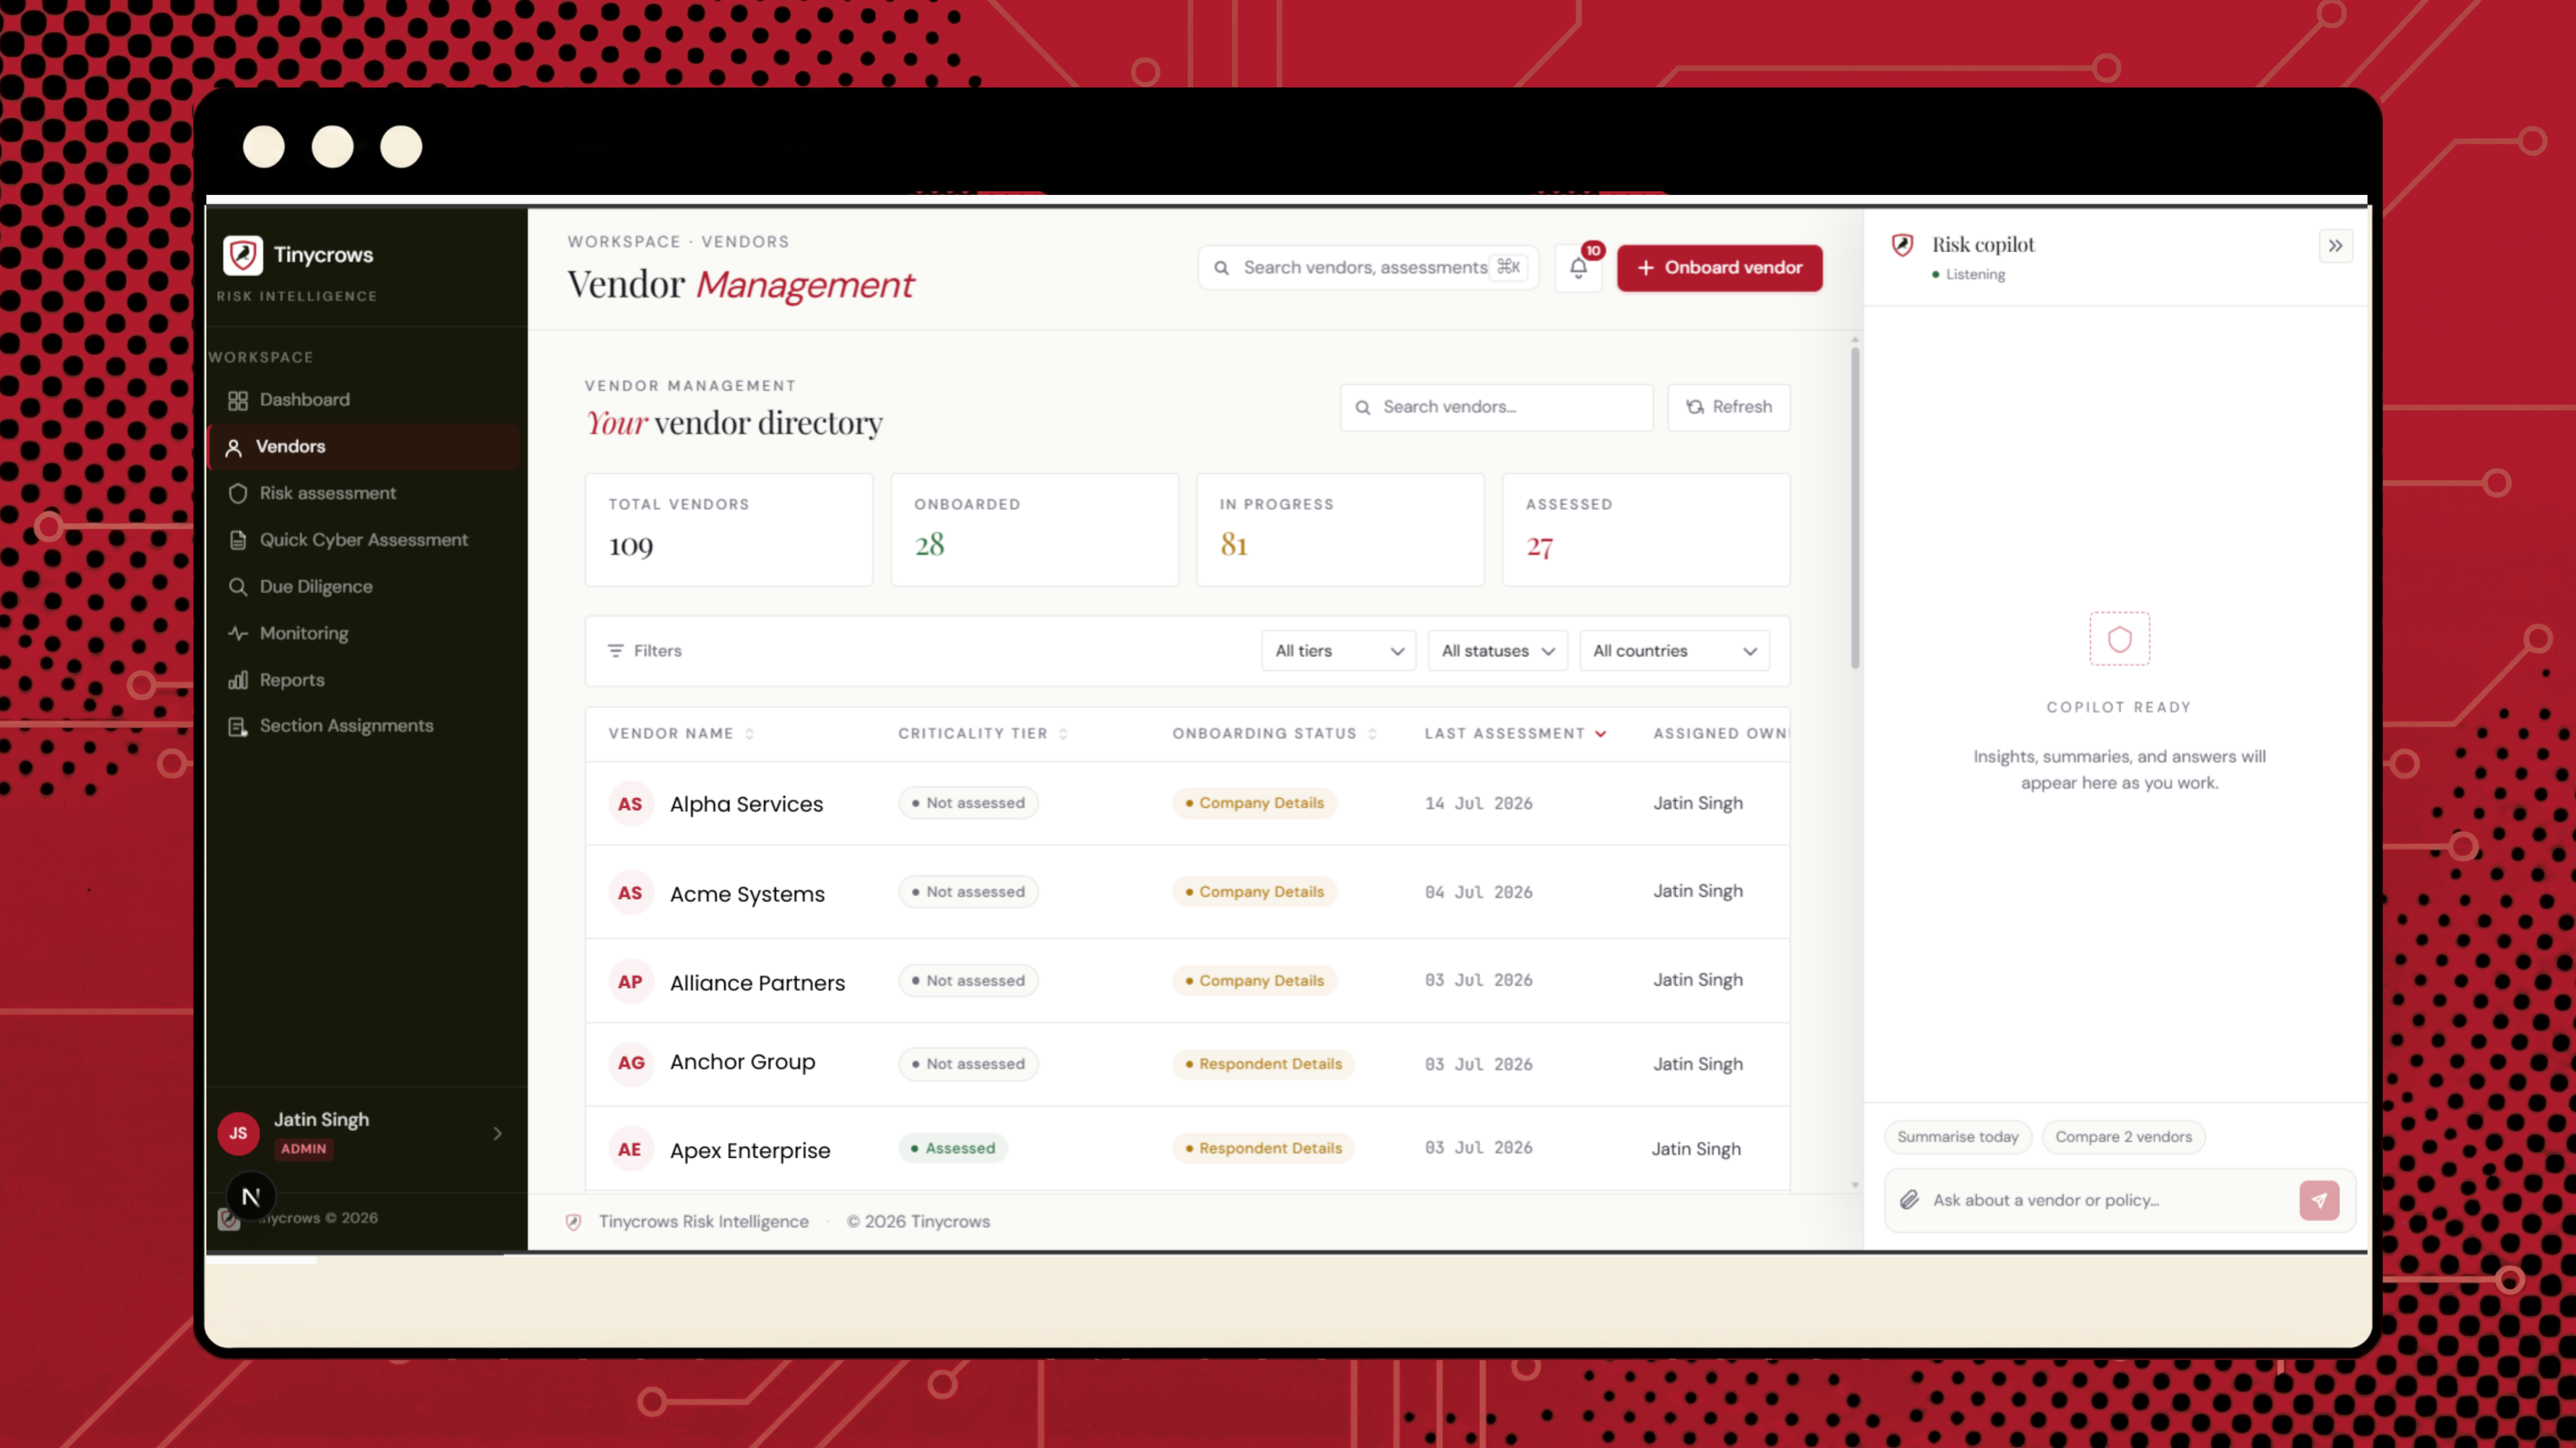
Vendor Discovery

Automatically discover vendors, map dependencies, and leverage AI-driven risk intelligence to accelerate third-party risk identification and assessment.
Tinycrows - Third-Party Risk Management (TPRM) - Vendor Discovery

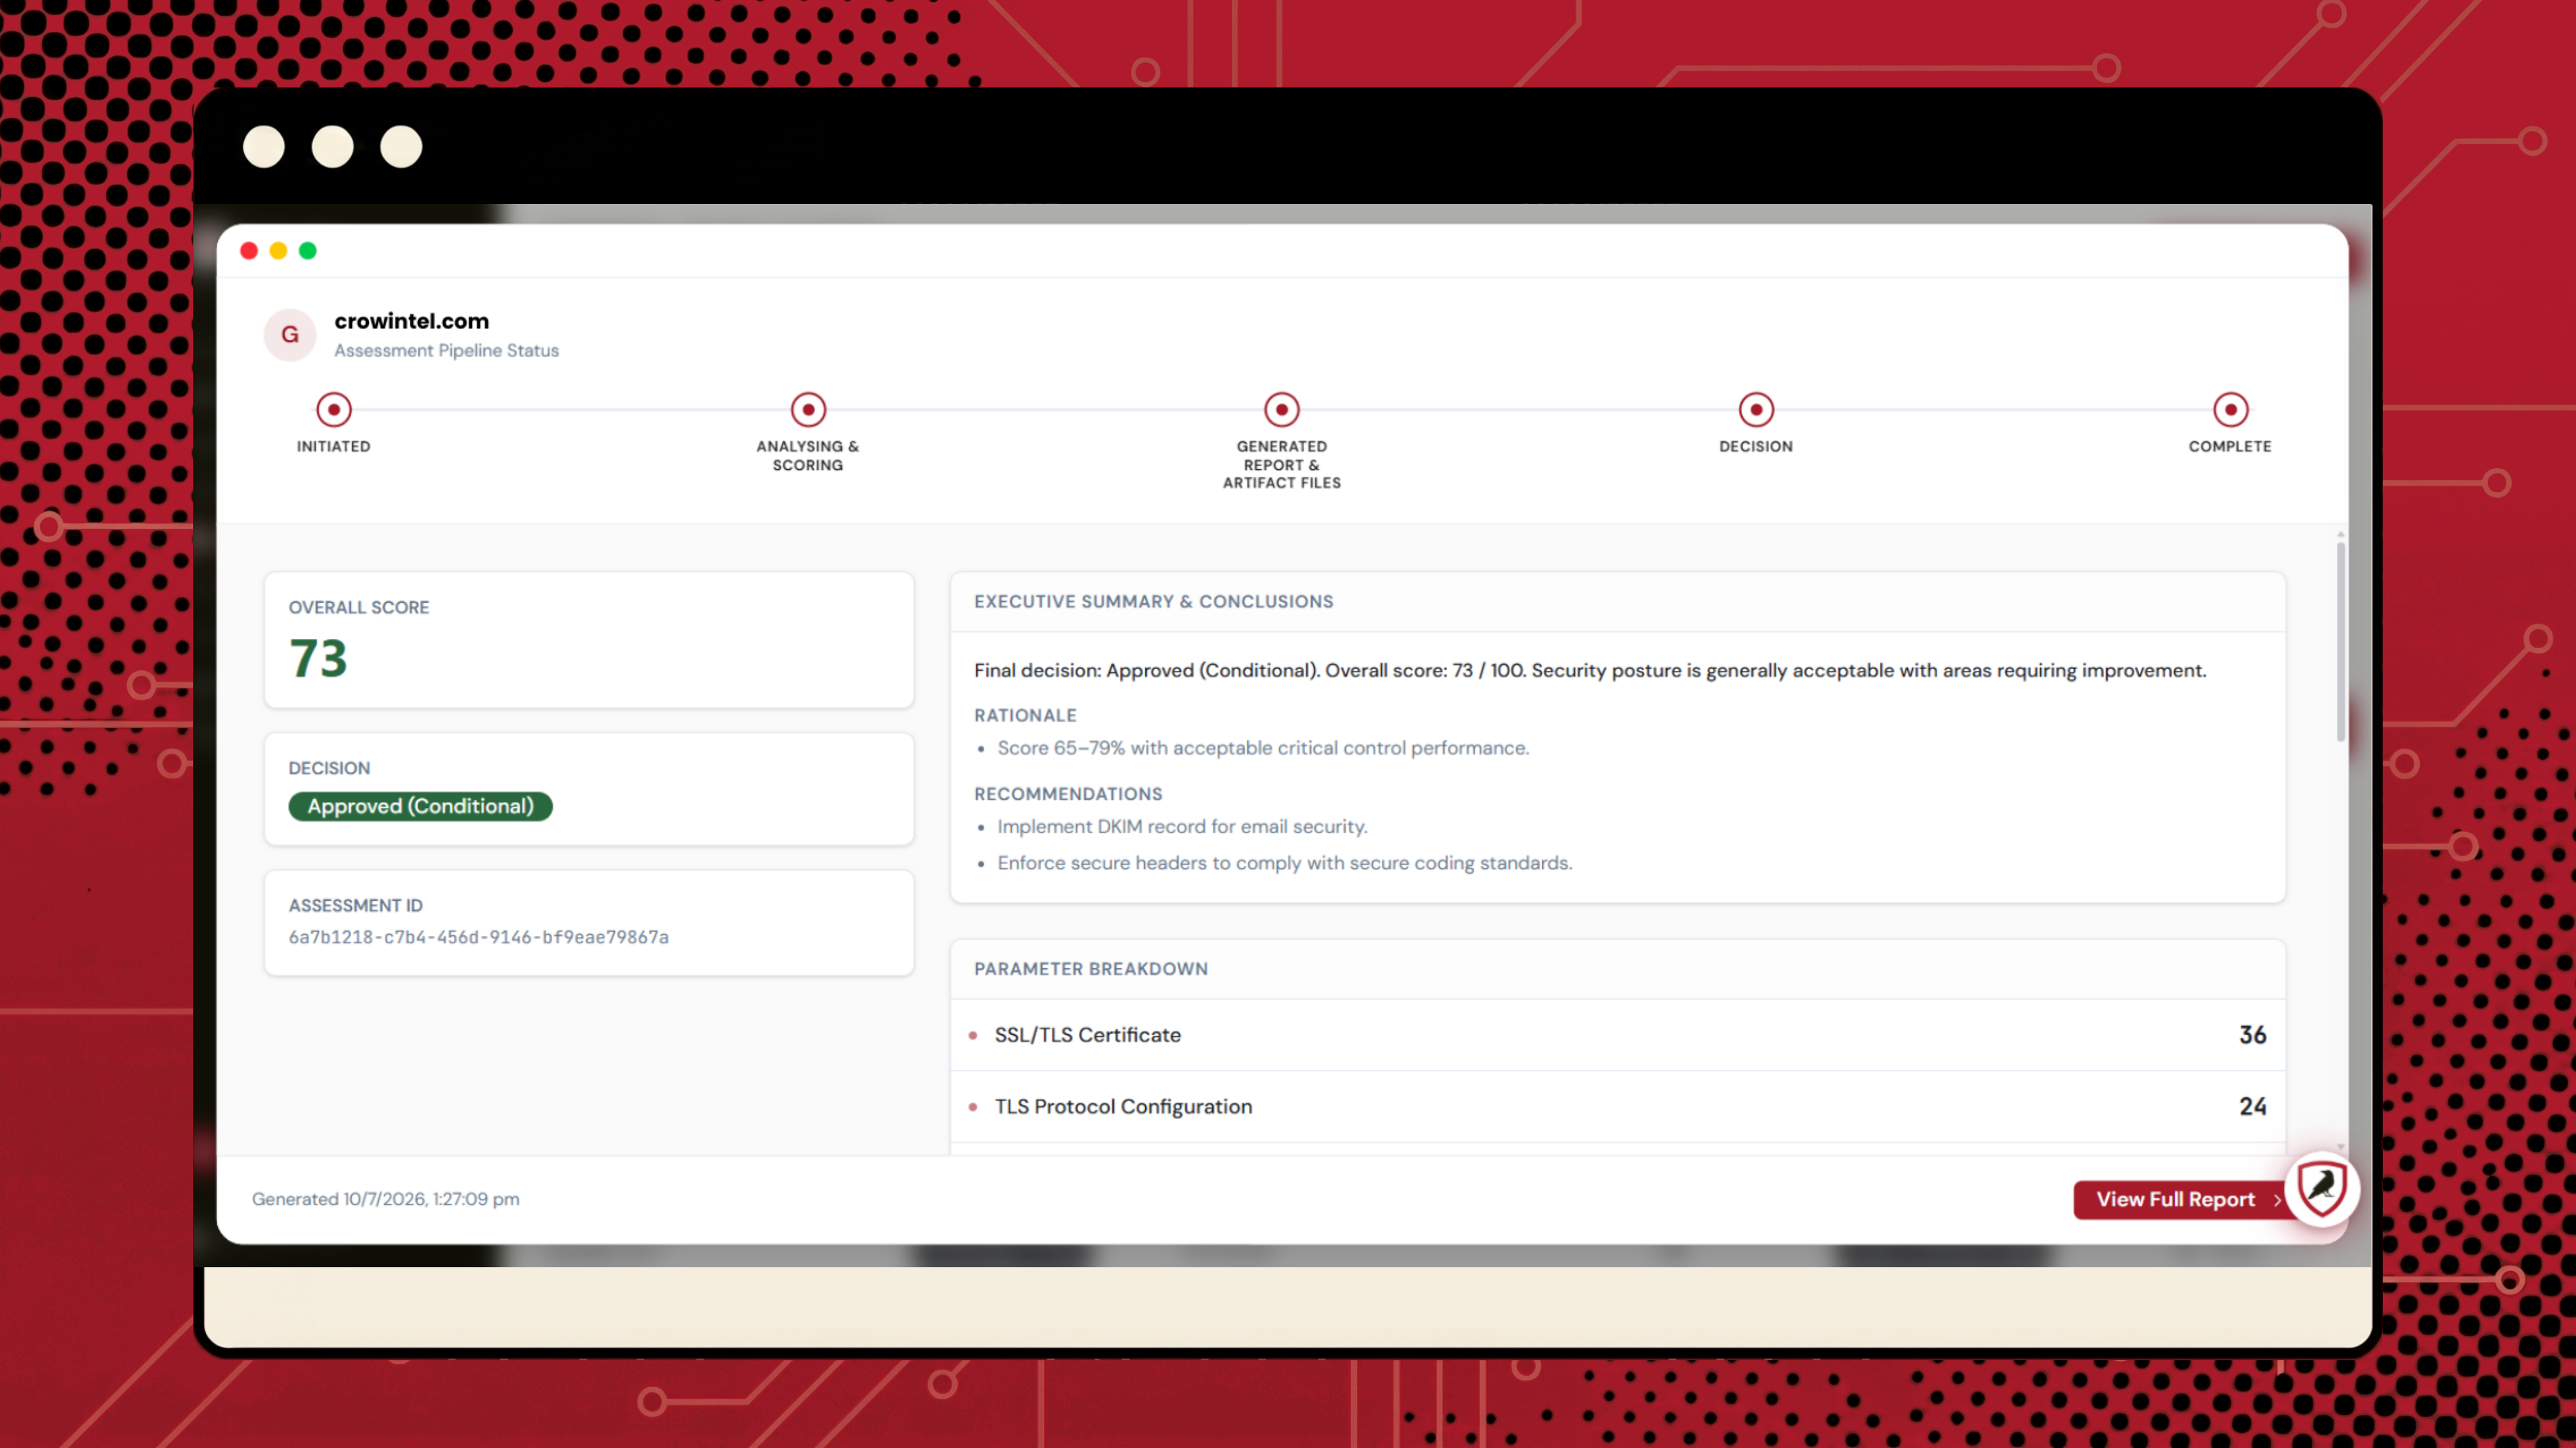
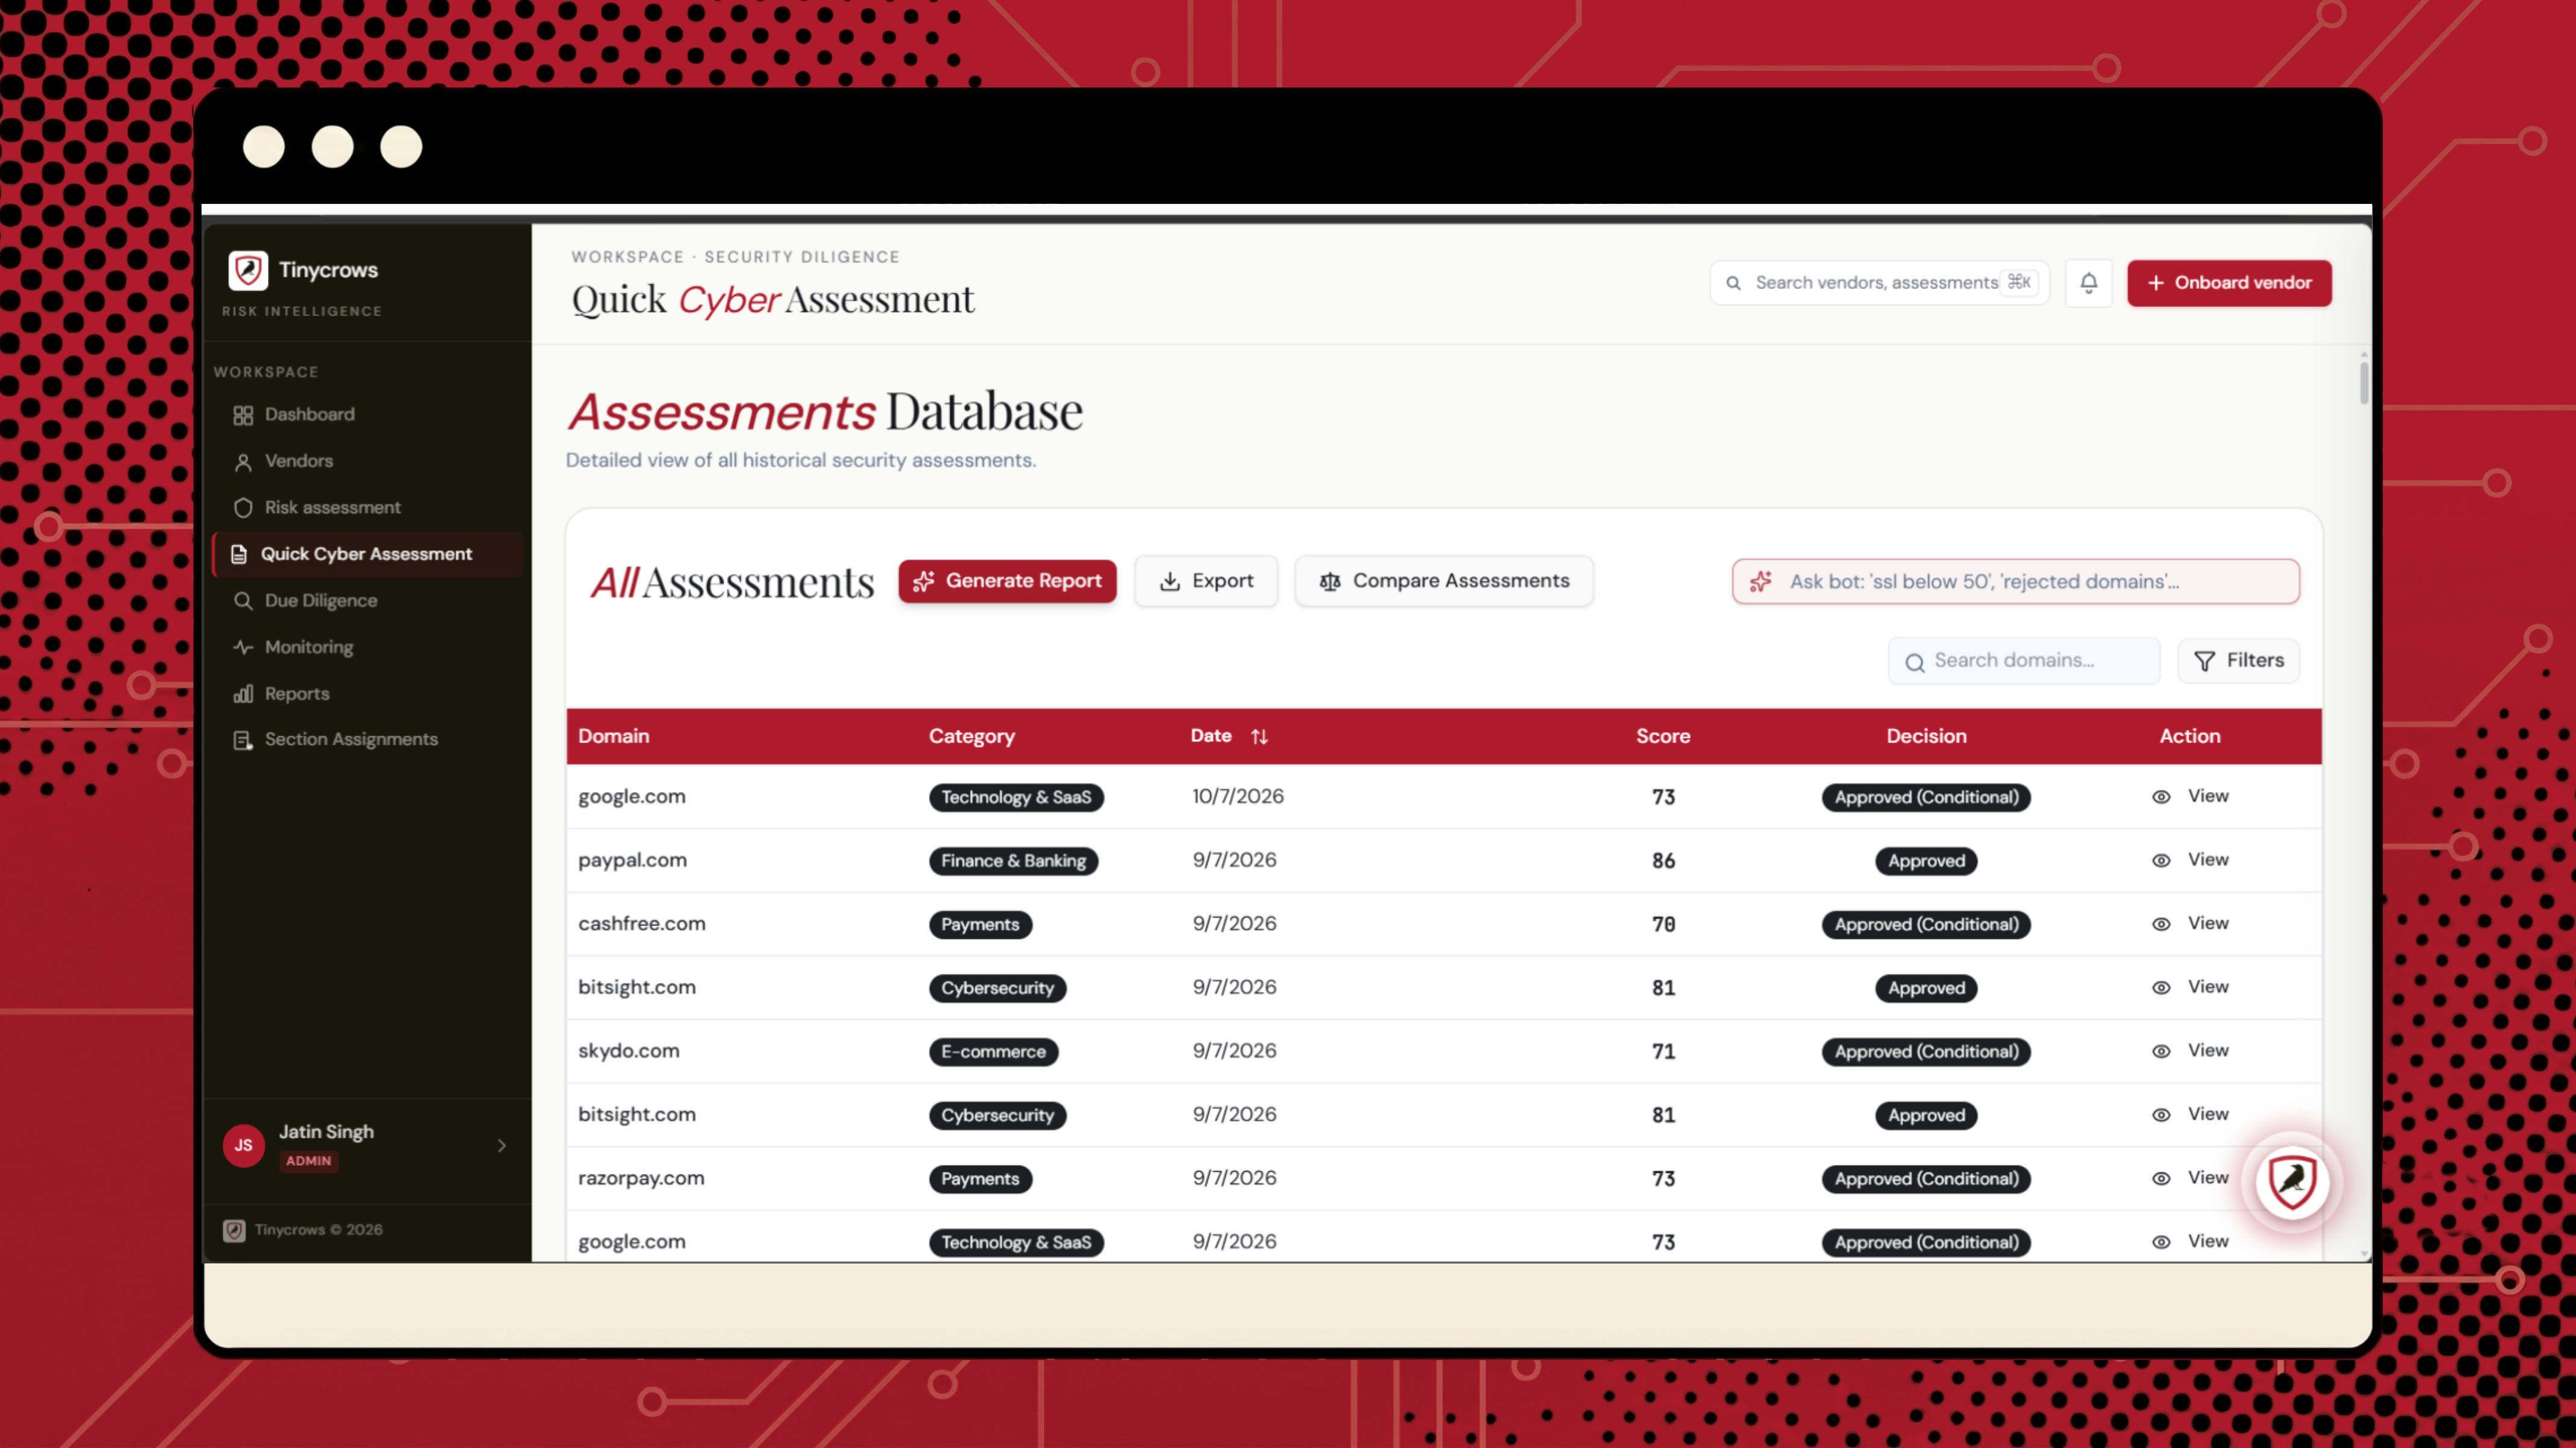
Risk Assessment

Automate vendor risk assessments, identify control gaps, prioritize risks, and streamline remediation with AI-powered security analysis.
Tinycrows - Third-Party Risk Management (TPRM) - Risk Assessment

Compliance Insights

This is some text inside of a div block.
Tinycrows - Third-Party Risk Management (TPRM) - Compliance Insights

Continuous Monitoring

Continuously monitor vendor security posture, detect emerging risks, and receive real-time alerts on third-party security changes.
Tinycrows - Third-Party Risk Management (TPRM) - Continuous Monitoring

Secure Offboarding

Ensure secure vendor offboarding through automated access reviews, compliance validation, audit trails, and risk-aware termination processes.
Tinycrows - Third-Party Risk Management (TPRM) - Secure Offboarding
Vendor Discovery

Vendor Discovery

Automatically discover vendors, map dependencies, and leverage AI-driven risk intelligence to accelerate third-party risk identification and assessment.
Risk Assessment

Risk Assessment

Automate vendor risk assessments, identify control gaps, prioritize risks, and streamline remediation with AI-powered security analysis.
Compliance Insights

Compliance Insights

This is some text inside of a div block.
Continuous Monitoring

Continuous Monitoring

Continuously monitor vendor security posture, detect emerging risks, and receive real-time alerts on third-party security changes.
Secure Offboarding

Secure Offboarding

Ensure secure vendor offboarding through automated access reviews, compliance validation, audit trails, and risk-aware termination processes.

Tinycrows was founded with a clear belief that cybersecurity must protect what truly matters to a business, not just what appears on a checklist.

Enhancing Collaboration between Cx

I was highly impressed with tinycrows' dedication to securing our fintech product. Their recommendations and prompt responses not only helped us resolve vulnerabilities but also prepared us for security due diligence.
Lokesh Jain
CTO, Finac
I am writing to express my sincere appreciation for your diligent work in completing the Security assessment for JPBL. Thanks for your effort! I appreciate your team completing this assessment in a timely manner.
Ravi Gali
CISO - Jio Payments Bank
I thoroughly enjoyed tinycrows commitment to securing our platform. It seemed more like a partnership and the feedback helps to make us a better organization and be more aware in our infrastructure and coding practices.
Jackie Popovich
Director, Roambee
I was highly impressed with tinycrows' dedication to securing our fintech product. Their recommendations and prompt responses not only helped us resolve vulnerabilities but also prepared us for security due diligence.
Lokesh Jain
CTO, Finac
I am writing to express my sincere appreciation for your diligent work in completing the Security assessment for JPBL. Thanks for your effort! I appreciate your team completing this assessment in a timely manner.
Ravi Gali
CISO - Jio Payments Bank
I thoroughly enjoyed tinycrows commitment to securing our platform. It seemed more like a partnership and the feedback helps to make us a better organization and be more aware in our infrastructure and coding practices.
Jackie Popovich
Director, Roambee
I was highly impressed with tinycrows' dedication to securing our fintech product. Their recommendations and prompt responses not only helped us resolve vulnerabilities but also prepared us for security due diligence.
Lokesh Jain
CTO, Finac
I am writing to express my sincere appreciation for your diligent work in completing the Security assessment for JPBL. Thanks for your effort! I appreciate your team completing this assessment in a timely manner.
Ravi Gali
CISO - Jio Payments Bank
I thoroughly enjoyed tinycrows commitment to securing our platform. It seemed more like a partnership and the feedback helps to make us a better organization and be more aware in our infrastructure and coding practices.
Jackie Popovich
Director, Roambee
I was highly impressed with tinycrows' dedication to securing our fintech product. Their recommendations and prompt responses not only helped us resolve vulnerabilities but also prepared us for security due diligence.
Lokesh Jain
CTO, Finac
I am writing to express my sincere appreciation for your diligent work in completing the Security assessment for JPBL. Thanks for your effort! I appreciate your team completing this assessment in a timely manner.
Ravi Gali
CISO - Jio Payments Bank
I was highly impressed with tinycrows' dedication to securing our fintech product. Their recommendations and prompt responses not only helped us resolve vulnerabilities but also prepared us for security due diligence.
Lokesh Jain
CTO, Finac
I am writing to express my sincere appreciation for your diligent work in completing the Security assessment for JPBL. Thanks for your effort! I appreciate your team completing this assessment in a timely manner.
Ravi Gali
CISO - Jio Payments Bank
What is TPRM?

TPRM is the process of identifying, assessing, monitoring and mitigating risks introduced by third-party vendors to ensure cybersecurity, compliance and operational resilience.

Why is TPRM important for financial institutions?

Banks and NBFCs rely heavily on vendors, making them vulnerable to supply chain attacks, data breaches and regulatory penalties.

 What is contiuous vendor monitoring?

It involves real-time tracking of vendor security posture, identifying vulnerabilities, threats and breaches proactively.

How does TPRM support regulatory compliance?

It ensures adherence to RBI, SEBI, ISO 27001, PCI-DSS and other regulatory frameworks through structured assessments and reporting.

Frequently Asked Questions

Find quick answers to common questions and make the most of Maps Explore’s key features, from traffic updates to emergency alerts

Send Your Message To Us

Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Attack Simulation

Attack Simulation & Red Teaming

Simulate real-world cyberattacks across the full attack lifecycle to test how your defenses perform against actual threats. Our continuous red teaming approach replicates techniques like ransomware, credential abuse, and privilege escalation to uncover real security gaps.
Surface Visibility

Attack Surface Visibility & Asset Discovery

Gain complete visibility into your attack surface by discovering all assets, including shadow IT, exposed services, and misconfigurations across your environment.
Lateral Movement

Attack Path & Lateral Movement Analysis

Understand how attackers move within your network. We map attack paths and identify how vulnerabilities can be chained to reach critical systems.
MITRE Mapping

Threat Intelligence, MITRE Mapping & Control Validation

Align your security testing with real-world threats using MITRE ATT&CK. Continuously validate how effectively your security controls detect and respond to attacks.
Secure Code Review

Risk Prioritization, Monitoring & Human Security

Focus on what truly matters by prioritizing risks based on real-world impact. Combine vulnerability prioritization, real-time monitoring, and phishing simulations to strengthen overall security.